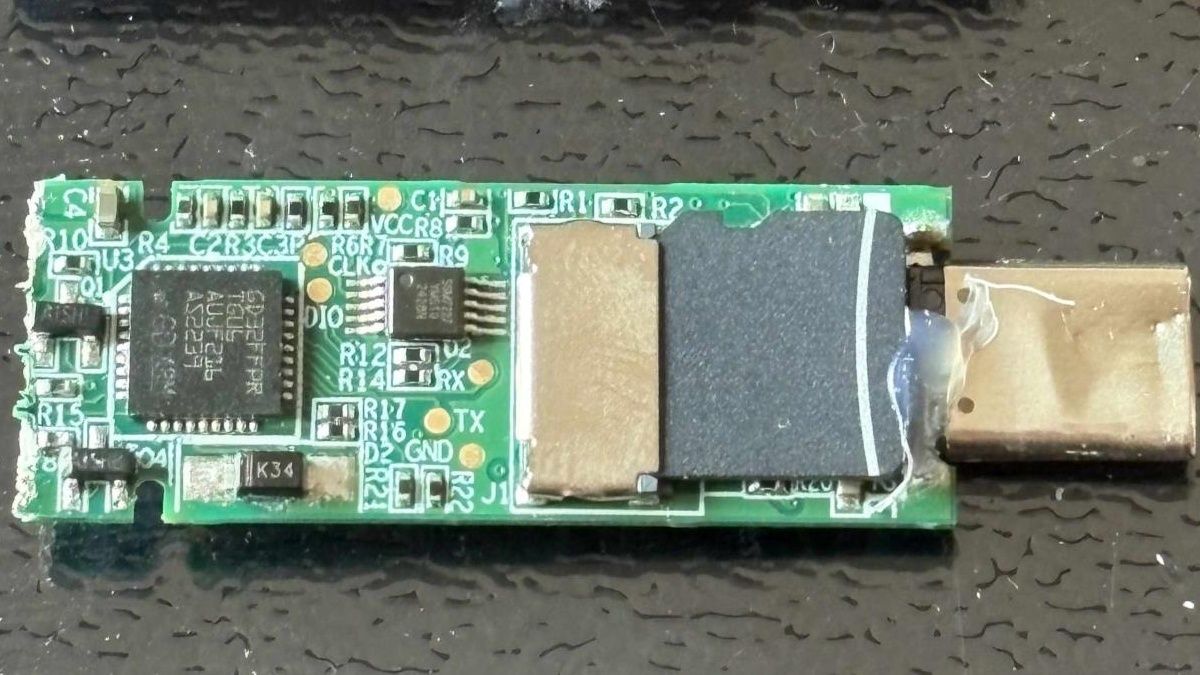
When purchasing hardware marketed for data security, buyers naturally assume that advanced features like hardware-level encryption and biometric locks protect their sensitive files. However, recent security findings highlight a startling gap between marketing claims and internal reality, demonstrating how easily consumer trust can be undermined by substandard manufacturing and overlooked design flaws.
The Anatomy of a Marketing Mirage
Security researcher Xusheng Li examined a fingerprint USB stick sold as an AES-256-encrypted device, only to discover that the hardware housed a plain, unencrypted micro SD card internally. The biometric fingerprint reader served a purely superficial function, acting merely as a switch to enable the USB connection rather than securing any actual data on the drive. Because the underlying storage lacked any real protection, bypassing the device was trivial for anyone with physical access.
This discrepancy raises fundamental questions about supply chain accountability and oversight in computing hardware. As one observer remarked, "If they are so disinterested in thier products that they didn't check if the primary feature was actually built correctly or not, then it's still a 100% on them. They shipped an unsecure, falsely advertised product to thier customer." Others noted the absurdity of relying on biometrics for core encryption, pointing out that "your biometrics should be your username, not your password."
Broader Flaws in Secure Storage
Subsequent investigations revealed that this issue extends far beyond a single product line. Follow-up analyses of other supposedly secure USB storage products and external solid-state drives uncovered hardcoded keys, backdoor accounts, and flawed software development kits across multiple vendors. In some cases, drives that did implement data encryption transmitted the correct password back over USB in plain text for verification purposes, creating a straightforward interception vector for malicious actors.
Artificial intelligence tools are increasingly utilized in reverse-engineering efforts to accelerate the discovery of these vulnerabilities. Researchers have demonstrated how automated tools can dissect protection schemes and extract fixed keys from proprietary software in a matter of minutes. These developments suggest that client-side validation mechanisms are inherently vulnerable and that marketing labels such as military-grade encryption offer little substitute for independent verification.
Moving Toward Reliable Protection
Incidents like these serve as a stark reminder that physical security features cannot substitute for robust, transparent encryption standards. While manufacturers frequently issue firmware updates or service advisories to address discovered flaws—often requiring inconvenient device replacements or data wipes—users seeking genuine privacy increasingly rely on software-based solutions like operating system encryption or standalone cryptographic containers.
As the industry grapples with these revelations, consumer advocates emphasize the importance of skepticism toward proprietary security claims. For critical data, relying on open-source standards and thoroughly vetted verification methods remains the most dependable defense against hidden vulnerabilities.

